The Compliance Brief
Practical guidance on security, certification, and supply chain trust — written by practitioners, not marketers.
Featured
The Evidence Problem: Why Businesses With Strong Security Controls Still Fail Compliance Audits
Latest Updates
The Evidence Problem: Why Businesses With Strong Security Controls Still Fail Compliance Audits
Controls that work but can't be proven might as well not exist. How to build an evidence pipeline — screenshots, exports, tickets, logs — that makes audit week boring. You configure a top-tier firewall to perfection. Your team locks down endpoints with enterprise-grade EDR, follows strict least-privilege access models, and patches vulnerabilities every week. By […]
Your Vendor’s Remote Access Is Your Biggest OT Risk: Building a Brokered Access Pattern Through the iDMZ
The unmanaged TeamViewer problem, why machine-builder VPNs bypass your segmentation, and a reference design for recorded, MFA-enforced, time-boxed vendor access. You trust your Original Equipment Manufacturers (OEMs) and external maintenance vendors to keep your plant floor running. They require remote access to troubleshoot programmable logic controllers (PLCs), update human-machine interfaces (HMIs), and tune critical machinery. […]
CIS Benchmarks for Manufacturers: Hardening Windows and Network Gear Without Breaking Legacy Industrial Software
Why Level 1 profiles are the right default, the settings most likely to break HMI and engineering software, and how to document deviations so auditors accept them. You apply standard Center for Internet Security (CIS) Benchmarks to harden your Windows systems and network switches. Your compliance checklist looks perfect on paper. Then, your human-machine interfaces […]
The Purdue Model Isn’t Dead — Your Implementation Is: Applying PERA in a Cloud-Connected Plant
Cloud MES, SaaS labeling platforms, and IIoT sensors don't break the Purdue Model — they raise the stakes for Level 3.5. How to route every modern IT/OT integration through an industrial DMZ without slowing the business down. Step into any modern manufacturing facility, and you will hear a common refrain from IT architects: “The Purdue […]
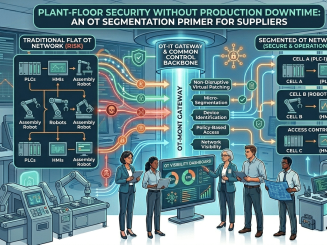
Plant-Floor Security Without Production Downtime: An OT Segmentation Primer for Suppliers
Practical network segmentation for manufacturing environments — IT/OT boundaries, conduit design, and how to satisfy auditors without touching a running line. Mention network segmentation to a plant manager, and they immediately worry about production halts. They picture dropped packets blocking human-machine interface (HMI) screens, interrupted programmable logic controller (PLC) commands, and thousands of dollars lost […]
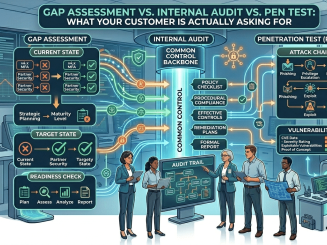
Gap Assessment vs. Internal Audit vs. Pen Test: What Your Customer Is Actually Asking For
A buyer's guide to assessment types, what each one proves, and which one your contract clause really requires. Your sales team flags a critical email from a major client demanding immediate proof of your security posture before signing a new contract. The buyer throws around high-stakes phrases, asking for an inspection, an assessment, or technical […]
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
The Evidence Problem: Why Businesses With Strong Security Controls Still Fail Compliance Audits
Controls that work but can't be proven might as well not exist. How to build an evidence pipeline — screenshots, exports, tickets, logs — that makes audit week boring. You configure a top-tier firewall to perfection. Your team locks down endpoints with enterprise-grade EDR, follows strict least-privilege access models, and patches vulnerabilities every week. By […]
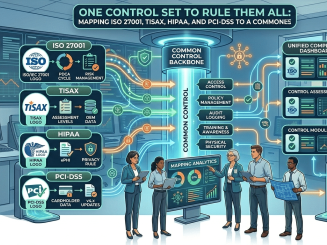
One Control Set to Rule Them All: Mapping ISO 27001, TISAX, HIPAA, and PCI-DSS to a Common Backbone
Our methodology for multi-framework efficiency — with a sample mapping of MFA, logging, and risk assessment requirements across all four. If your company processes credit cards, handles automotive designs, and manages defense parts, your security team faces a compliance nightmare. You must pass a PCI-DSS audit in Q1, update your TISAX label in Q2, verify […]
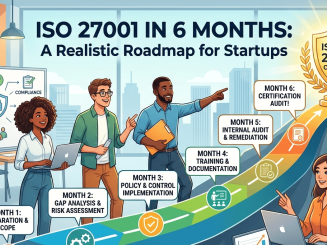
ISO 27001 in 6 Months: A Realistic Roadmap for Startups
Month-by-month breakdown from kickoff to Stage 2 audit — what to do, what to skip, and where companies actually lose time (hint: it's the risk assessment and the evidence backlog, not the policies). Many tech startups view ISO 27001 compliance as a slow, multi-year administrative burden. They assume that building an Information Security Management System […]
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
Your IATF Auditor Is About to Ask About Ransomware: Cyber Contingency Planning Under IATF 16949
Why business continuity expectations now reach into cybersecurity, and how to align your IT/OT contingency plans with your QMS before the next surveillance audit. This narrow perspective creates an immediate risk of a failed audit. IATF 16949 section 6.1.2.3 enforces strict cyber contingency mandates. Auditors no longer accept basic paper evacuation routes. They actively test […]
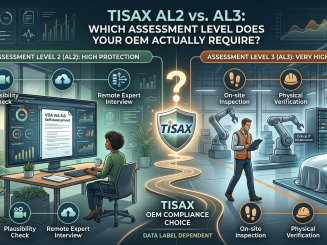
TISAX AL2 vs. AL3: Which Assessment Level Does Your OEM Actually Require?
How to read your customer's requirement letter, what changes between levels (plausibility check vs. on-site assessment), and how prototype protection scope can surprise you. IIf you supply parts to European automotive brands, your partners will eventually demand a formal TISAX label. Many manufacturing executives look at the extensive compliance handbooks and assume they can choose […]
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
Your Vendor’s Remote Access Is Your Biggest OT Risk: Building a Brokered Access Pattern Through the iDMZ
The unmanaged TeamViewer problem, why machine-builder VPNs bypass your segmentation, and a reference design for recorded, MFA-enforced, time-boxed vendor access. You trust your Original Equipment Manufacturers (OEMs) and external maintenance vendors to keep your plant floor running. They require remote access to troubleshoot programmable logic controllers (PLCs), update human-machine interfaces (HMIs), and tune critical machinery. […]
CIS Benchmarks for Manufacturers: Hardening Windows and Network Gear Without Breaking Legacy Industrial Software
Why Level 1 profiles are the right default, the settings most likely to break HMI and engineering software, and how to document deviations so auditors accept them. You apply standard Center for Internet Security (CIS) Benchmarks to harden your Windows systems and network switches. Your compliance checklist looks perfect on paper. Then, your human-machine interfaces […]
The Purdue Model Isn’t Dead — Your Implementation Is: Applying PERA in a Cloud-Connected Plant
Cloud MES, SaaS labeling platforms, and IIoT sensors don't break the Purdue Model — they raise the stakes for Level 3.5. How to route every modern IT/OT integration through an industrial DMZ without slowing the business down. Step into any modern manufacturing facility, and you will hear a common refrain from IT architects: “The Purdue […]
Plant-Floor Security Without Production Downtime: An OT Segmentation Primer for Suppliers
Practical network segmentation for manufacturing environments — IT/OT boundaries, conduit design, and how to satisfy auditors without touching a running line. Mention network segmentation to a plant manager, and they immediately worry about production halts. They picture dropped packets blocking human-machine interface (HMI) screens, interrupted programmable logic controller (PLC) commands, and thousands of dollars lost […]
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
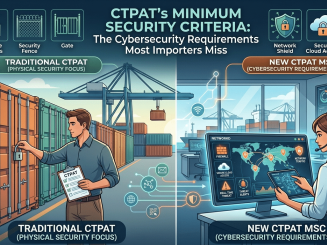
CTPAT’s Minimum Security Criteria: The Cybersecurity Requirements Most Importers Miss
A walk through the cyber portions of the MSC — access control, system protections, and what validators actually look for during site visits. If your business moves goods across borders, you rely on the Customs-Trade Partnership Against Terrorism (CTPAT) program to skip long border delays. Yet, many global logistics teams still view this certification as […]
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
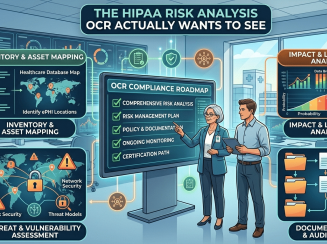
The HIPAA Risk Analysis OCR Actually Wants to See
The single most-cited gap in OCR enforcement actions — and a template for doing it right: scope, asset inventory, threat identification, likelihood/impact, and documented risk decisions. If your manufacturing or logistics firm handles health-related data, employee benefits portals, or medical supply chains, you fall under HIPAA regulations. Yet, many executive teams view healthcare compliance as […]
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
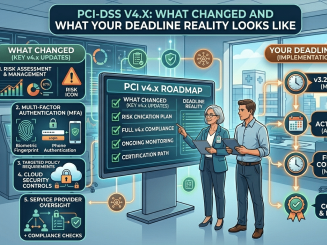
PCI-DSS v4.x: What Changed and What Your Deadline Reality Looks Like
Future-dated requirements that are now in force, the customized approach option, and how to shrink your CDE before you start writing checks. If your business processes credit card data, your compliance landscape just shifted. The legacy version 3.2.1 has retired, making the transition to the updated v4.x framework completely mandatory. Many manufacturing, defense, and automotive […]
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
Gap Assessment vs. Internal Audit vs. Pen Test: What Your Customer Is Actually Asking For
A buyer's guide to assessment types, what each one proves, and which one your contract clause really requires. Your sales team flags a critical email from a major client demanding immediate proof of your security posture before signing a new contract. The buyer throws around high-stakes phrases, asking for an inspection, an assessment, or technical […]
Search Posts
Framework Deadline Tracker
Enforcement Watch