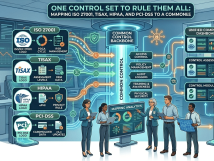
Our methodology for multi-framework efficiency — with a sample mapping of MFA, logging, and risk assessment requirements across all four.
If your company processes credit cards, handles automotive designs, and manages defense parts, your security team faces a compliance nightmare. You must pass a PCI-DSS audit in Q1, update your TISAX label in Q2, verify ISO 27001 compliance in Q3, and prove HIPAA alignment by Q4.
Operating under distinct compliance silos forces your engineering team to spend all year taking screenshots, chasing down logs, and filling out repetitive questionnaires.
Managing multiple security frameworks individually wastes administrative budgets and burns out your engineering staff. To reclaim your time and scale your business securely, you must combine your requirements by mapping ISO 27001, TISAX, HIPAA, and PCI-DSS to a common backbone.
The Strategic Fix: Unified Control Frameworks
Most compliance frameworks demand the exact same security principles at their core. Whether a regulation calls it an access list, a permission profile, or a privilege boundary, the underlying technical requirement remains identical: lock down user privileges.
Instead of writing individual procedures for every certification, build a single, centralized Unified Control Framework (UCF). When you configure a technical baseline—such as enforcing multi-factor authentication (MFA)—you satisfy four separate audit checkpoints simultaneously.
The core operational reality stands clear: Engineers should build to one rigorous technical standard, not to individual compliance checklists.
Three Pitfalls of Running Siloed Compliance Audits
Organizations fall behind on security implementations because they treat every new framework certification as a distinct, standalone project. This traditional approach triggers three critical failures:
- Massive Operational Redundancy: Your team performs identical tasks—like quarterly vulnerability scanning—four separate times because different compliance managers do not share data artifacts.
- Conflicting Technical Baselines: Siloed engineering teams build custom configurations to pass an isolated PCI audit, accidentally breaking a specific access rule required to maintain your TISAX label.
- Endless Administrative Screen Fatigue: Engineers spend more time collecting manual screenshots for multiple compliance platforms than actively defending your plant floor against cyber threats.
Your Four-Step Roadmap to a Unified Security Backbone
You can consolidate your overlapping certifications without disrupting production by mapping your compliance obligations directly into a centralized security backbone:
- Select Your Anchor Standard: Establish a robust, globally recognized framework like ISO 27001 or NIST SP 800-53 as your primary structural foundation.
- Map Your Overlapping Safeguards: Identify the shared core controls across your framework list. For instance, link access control rules, incident response plans, and backup protocols into single, shared policies.
- Isolate Unique Framework Outliers: Identify the highly specific requirements that do not overlap. Isolate PCI-DSS cardholder data boundaries or HIPAA medical privacy rules, applying them only to those specific data environments.
- Automate a Unified Evidence Repository: Feed your system logs, configuration proofs, and patch records into one centralized evidence folder. Provide this single data source to all arriving auditors.
Simplify Your Audit Burden with Cyber Frontline
At Cyber Frontline, we eliminate compliance fatigue for high-stakes manufacturing and defense suppliers. We help your business simplify operations by mapping ISO 27001, TISAX, HIPAA, and PCI-DSS to a common backbone. We deploy practitioner-led engineering strategies that satisfy multiple auditors at once, protecting your data infrastructure while keeping your production lines moving forward.