Future-dated requirements that are now in force, the customized approach option, and how to shrink your CDE before you start writing checks.
If your business processes credit card data, your compliance landscape just shifted. The legacy version 3.2.1 has retired, making the transition to the updated v4.x framework completely mandatory.
Many manufacturing, defense, and automotive suppliers treat payment compliance as a minor IT issue. Failing to meet these updated criteria triggers massive monthly fines, transaction freezes, and merchant contract cancellations. To protect your cash flow, you must grasp exactly PCI-DSS v4.x: What Changed and What Your Deadline Reality Looks Like.
The Strategic Shift: Continuous Security vs. Annual Checklists
The previous version allowed organizations to treat compliance as a point-in-time exercise. Teams hardened systems right before the auditor arrived and ignored controls for the rest of the year.
PCI-DSS v4.x eliminates this habit. While the framework allows you to customize your security controls, it demands immutable proof of continuous, everyday operational health. Auditors now evaluate your ongoing habits, not your annual preparation scripts.
Three Major Changes Requiring Immediate Attention
The transition to v4.x introduces over 60 new requirements. For suppliers, these three structural shifts require immediate engineering action:
- Strict Multi-Factor Authentication (MFA): You must enforce MFA for all access into the cardholder data environment (CDE), including internal employees, not just remote administrators.
- Automated Log Reviews: The standard replaces manual log checks. Your team must deploy automated tools—like a SIEM—to analyze security logs and trigger real-time alerts.
- Anti-Skimming Script Protections: Hackers frequently target web payment scripts. Version 4.x mandates that you inventory and actively validate the integrity of all scripts running on your payment pages.
Your Framework to Meet the Mandatory Timelines
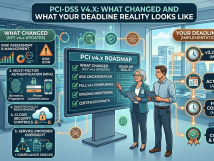
The most challenging, future-dated requirements are strictly mandatory. You must execute this three-step roadmap to achieve compliance before your next assessment:
- Run a Delta Assessment: Run a focused gap assessment to map your current technical controls directly against the new v4.x mandates.
- Deploy Automated Monitoring: Update your logging configurations. Ensure your systems actively monitor, flag, and record all administrative access attempts into your CDE boundaries.
- Audit External Vendor Connections: Review your partner networks. Ensure every contractor accessing your system complies with the new, strict multi-factor authentication rules.
Secure Your Payments with Cyber Frontline
At Cyber Frontline, we strip the complexity out of payment card compliance. We help your organization navigate PCI-DSS v4.x: What Changed and What Your Deadline Reality Looks Like. We deploy practitioner-led engineering strategies that satisfy QSAs, harden your payment infrastructure, and protect your revenue streams without disrupting your operations.