The Compliance Brief
Practical guidance on security, certification, and supply chain trust — written by practitioners, not marketers.
Featured
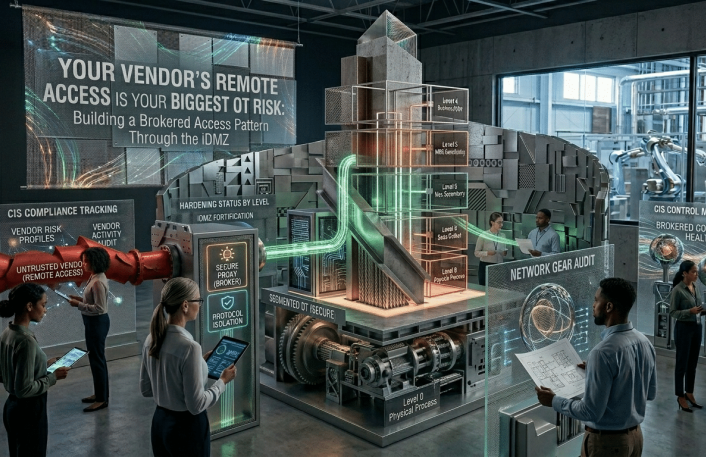
Your Vendor’s Remote Access Is Your Biggest OT Risk: Building a Brokered Access Pattern Through the iDMZ
Latest Updates
One Control Set to Rule Them All: Mapping ISO 27001, TISAX, HIPAA, and PCI-DSS to a Common Backbone
Our methodology for multi-framework efficiency — with a sample mapping of MFA, logging, and risk assessment requirements across all four. If your company processes credit cards, handles automotive designs, and manages defense parts, your security team faces a compliance nightmare. You must pass a PCI-DSS audit in Q1, update your TISAX label in Q2, verify […]
PCI-DSS v4.x: What Changed and What Your Deadline Reality Looks Like
Future-dated requirements that are now in force, the customized approach option, and how to shrink your CDE before you start writing checks. If your business processes credit card data, your compliance landscape just shifted. The legacy version 3.2.1 has retired, making the transition to the updated v4.x framework completely mandatory. Many manufacturing, defense, and automotive […]
The HIPAA Risk Analysis OCR Actually Wants to See
The single most-cited gap in OCR enforcement actions — and a template for doing it right: scope, asset inventory, threat identification, likelihood/impact, and documented risk decisions. If your manufacturing or logistics firm handles health-related data, employee benefits portals, or medical supply chains, you fall under HIPAA regulations. Yet, many executive teams view healthcare compliance as […]
CTPAT’s Minimum Security Criteria: The Cybersecurity Requirements Most Importers Miss
A walk through the cyber portions of the MSC — access control, system protections, and what validators actually look for during site visits. If your business moves goods across borders, you rely on the Customs-Trade Partnership Against Terrorism (CTPAT) program to skip long border delays. Yet, many global logistics teams still view this certification as […]
Your IATF Auditor Is About to Ask About Ransomware: Cyber Contingency Planning Under IATF 16949
Why business continuity expectations now reach into cybersecurity, and how to align your IT/OT contingency plans with your QMS before the next surveillance audit. This narrow perspective creates an immediate risk of a failed audit. IATF 16949 section 6.1.2.3 enforces strict cyber contingency mandates. Auditors no longer accept basic paper evacuation routes. They actively test […]
TISAX AL2 vs. AL3: Which Assessment Level Does Your OEM Actually Require?
How to read your customer's requirement letter, what changes between levels (plausibility check vs. on-site assessment), and how prototype protection scope can surprise you. IIf you supply parts to European automotive brands, your partners will eventually demand a formal TISAX label. Many manufacturing executives look at the extensive compliance handbooks and assume they can choose […]
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
Search Posts
Framework Deadline Tracker
Enforcement Watch
Latest Updates
Search Posts
Framework Deadline Tracker
Enforcement Watch